

TCP OS Spoofing (Anti TCP/OS Fingerprinting)
Make your proxy look like the device your browser pretends to be. Websites then see one story: the same system in your browser and on the network.
You need: the Premium plan or higher. On Free and Basic, Change answers "This function supported for higher plan. Please upgrade to use!".
In short
Every system starts a network connection in its own way. This is its TCP fingerprint. Sites compare it with the system your browser reports.
Your proxy box runs Linux. A Windows browser behind it looks wrong: Windows in the browser, Linux on the network.
Pick Windows, macOS, iPhone, iPad or Android for each modem, or copy any real device into a custom profile in one minute.
How a website spots the mismatch
Watch one connection from your browser to a website, first with spoofing off, then on.
Your browser
User-Agent
Windows NT 10.0; Win64; x64SaysWindows
XProxy box
The box runs Linux
TCP/OS spoofing: onProfile: Windows 11 (win1)
website.example
Compares the two
Browser saysWindows
Packet says…Linux / AndroidWindows
Windows score: 52%
Match: looks like a real Windows PC
The first packet (SYN)leaving the box
Looks like: Windows- Hop counter (TTL)
- 128
- Window size
- 65535
- Segment size (MSS)
- 1452kept
- Window scale
- 8
- Option order
- MSSNOPScaleNOPNOPSACK
Windows in the browser, Windows on the network: the stories match.
Illustration · values from a real captureThe numbers in the animation are real. They come from the two BrowserLeaks captures below.
What websites see
Example: your browser profile says Windows 11.
Spoofing off
Does not match
Spoofing on, Windows 11 profile
Same story
Your User-Agent does not change. Spoofing only changes the network side. The box changes how each new connection starts (its first packet) and keeps the rest of that device's traffic in line with the profile.
Profiles you can pick
Pick the one that matches the system in your browser profile.
| Profile ID | Name |
|---|---|
win1 | Windows 11 (24H2 and newer) |
win2 | Windows 10 / Windows 11 (up to 23H2) |
win3 | Windows 7 / 8.1 (old PC) |
mac1 | macOS 26 and newer |
ipad1 | iPad (iPadOS 26 and newer) |
ios1 | iPhone (iOS 17 / 18) |
ios2 | iPhone (iOS 26 and newer) |
android1 | Samsung Galaxy (Android) |
android2 | Google Pixel (Android) |
linux | Linux (default, no spoofing) |
Your system is not here? Add your own profile from a real device.
Set a profile on your devices
Step 1 of 5
Spoofing needs one setting first. In Proxy Management, click Proxy Settings and open the Advanced tab. Scroll down to Disable WebRTC Leak and turn on 1 Force WebRTC use Dongle network.
Add your own profile
You are not limited to our list. Copy any real phone, tablet or computer, including a new OS version released yesterday: open a page on xproxy.io on that device, then import its fingerprint into your panel with a one-time code. It works at once, with no update and no restart. Most proxy tools only offer a fixed list; with XProxy your profiles always match the devices your customers really use.
- Copy the exact model and OS version your browser profiles claim, for example an iPhone on the newest iOS or a specific Samsung.
- Paste a p0f signature instead, if you already have one.
- Compare 2 to 6 profiles side by side before you use them.
Step 1 of 7
Take the phone or computer you want to copy. Turn off any VPN or proxy on it. Open xproxy.io/tools/capture-fingerprint.
Click Capture this device 1.
Check it yourself
Check anonymity in the panel is the quickest test. To see what a website sees, use BrowserLeaks:
- Pick the profile for the device (steps above) and set the same system in your browser profile, for example Windows.
- Open that browser profile with the proxy port of the device.
- Go to browserleaks.com/tcp.
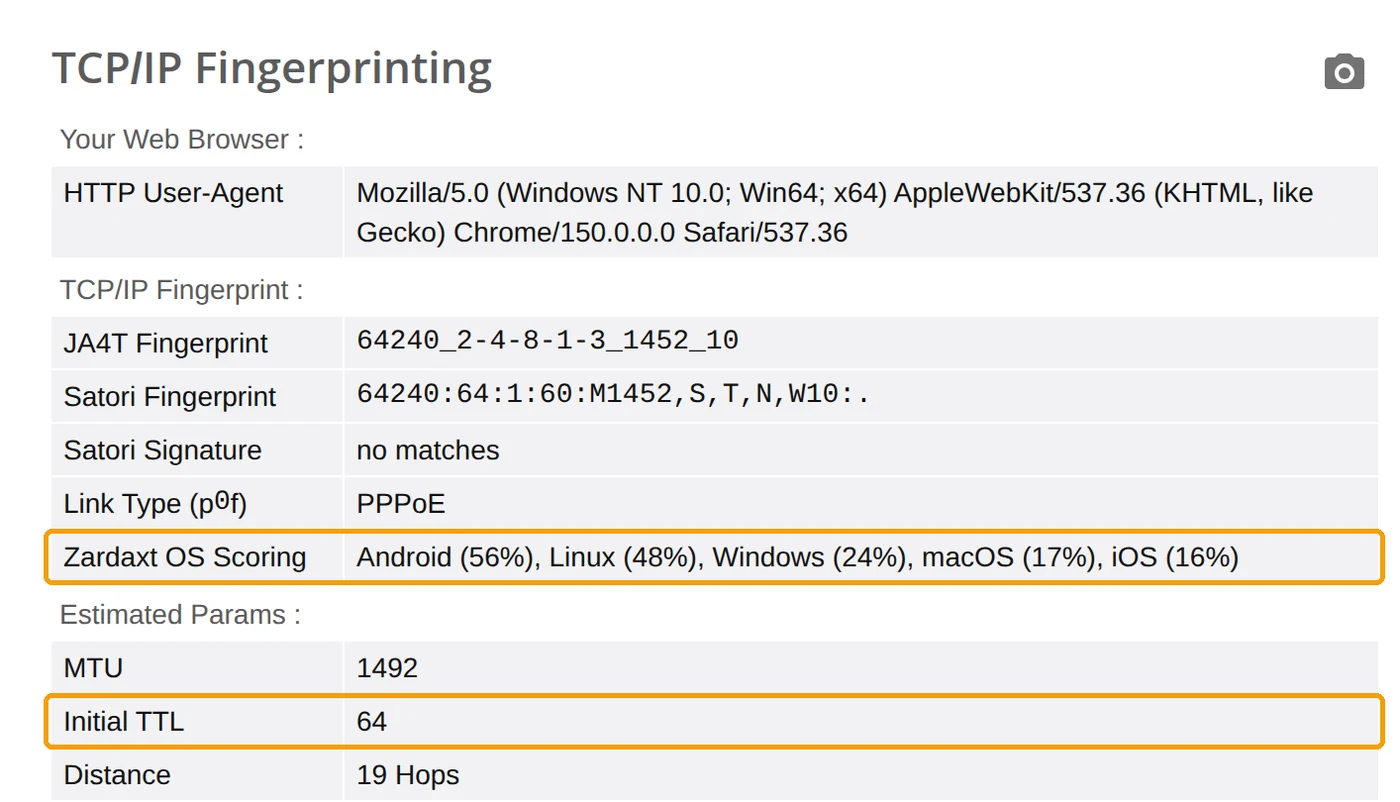
- Compare HTTP User-Agent (the system your browser says) with Zardaxt OS Scoring and Initial TTL (the system the connection looks like). They should name the same system.
Spoofing off
Spoofing on, Windows 11 profile
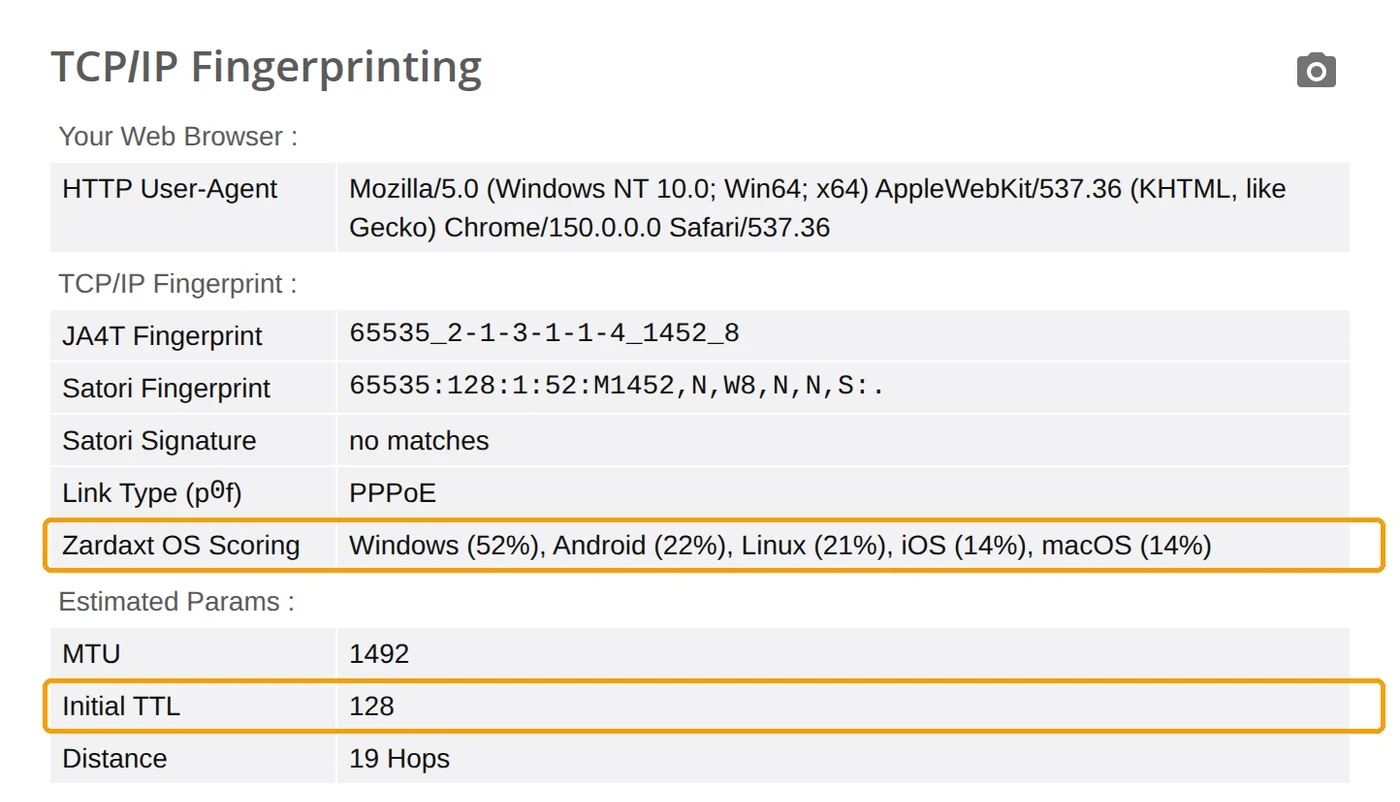
Real BrowserLeaks captures from a lab test, not from a customer device: the same Linux host and the same Windows browser, once through a plain proxy and once through the XProxy TCP OS engine with the Windows 11 profile (win1). The percentages are BrowserLeaks' own estimate and change from network to network. This BrowserLeaks panel shows no IP address, so nothing was edited in the pictures except the amber frames.
More pages to try through the proxy:
- BrowserLeaks IP: IP and environment leaks.
- Incolumitas: proxy and VPN checks.
- WITCH by valdikss: TCP/IP tests.
Good practice
- Tell one story. Browser profile system, timezone, language and TCP profile should agree.
- Do not switch often. Keep one profile for the same account.
Limits
- Some networks (carrier-grade NAT, firewalls, deep packet inspection) can change TCP details on the way. Check anonymity shows what websites really see.
- If the spoofing engine stops, connections go out unchanged. They are not blocked.
Android phones as proxy devices
When an Android phone running XProxy NextGen is itself the proxy device, its connections are made by Android's own network stack. Rewriting that stack needs root access and changes to the phone's system, which XProxy does not do: it keeps your phones unrooted, safe to update and covered by their warranty. So the OS icon does not show on Android phone rows.
That traffic already looks like what it is: a real Android phone on a mobile network. If your browser profiles claim Windows or iPhone, use a dongle, CPE or XLE modem with the matching profile instead.
Questions
Tests still show Linux. Why?
Click Check anonymity and read the lines marked Check or Problem. If the profile is set but a network on the way changes the connection, try another carrier or avoid extra VPN layers on the path.
Will websites still detect my proxy?
Some may. They look at many signals. TCP OS Spoofing removes one of them; What websites check covers the others (WebRTC, DNS, UDP, TTL, timezone).
What next?
Test the whole modem in one click, then set the same system in your browser tool.